
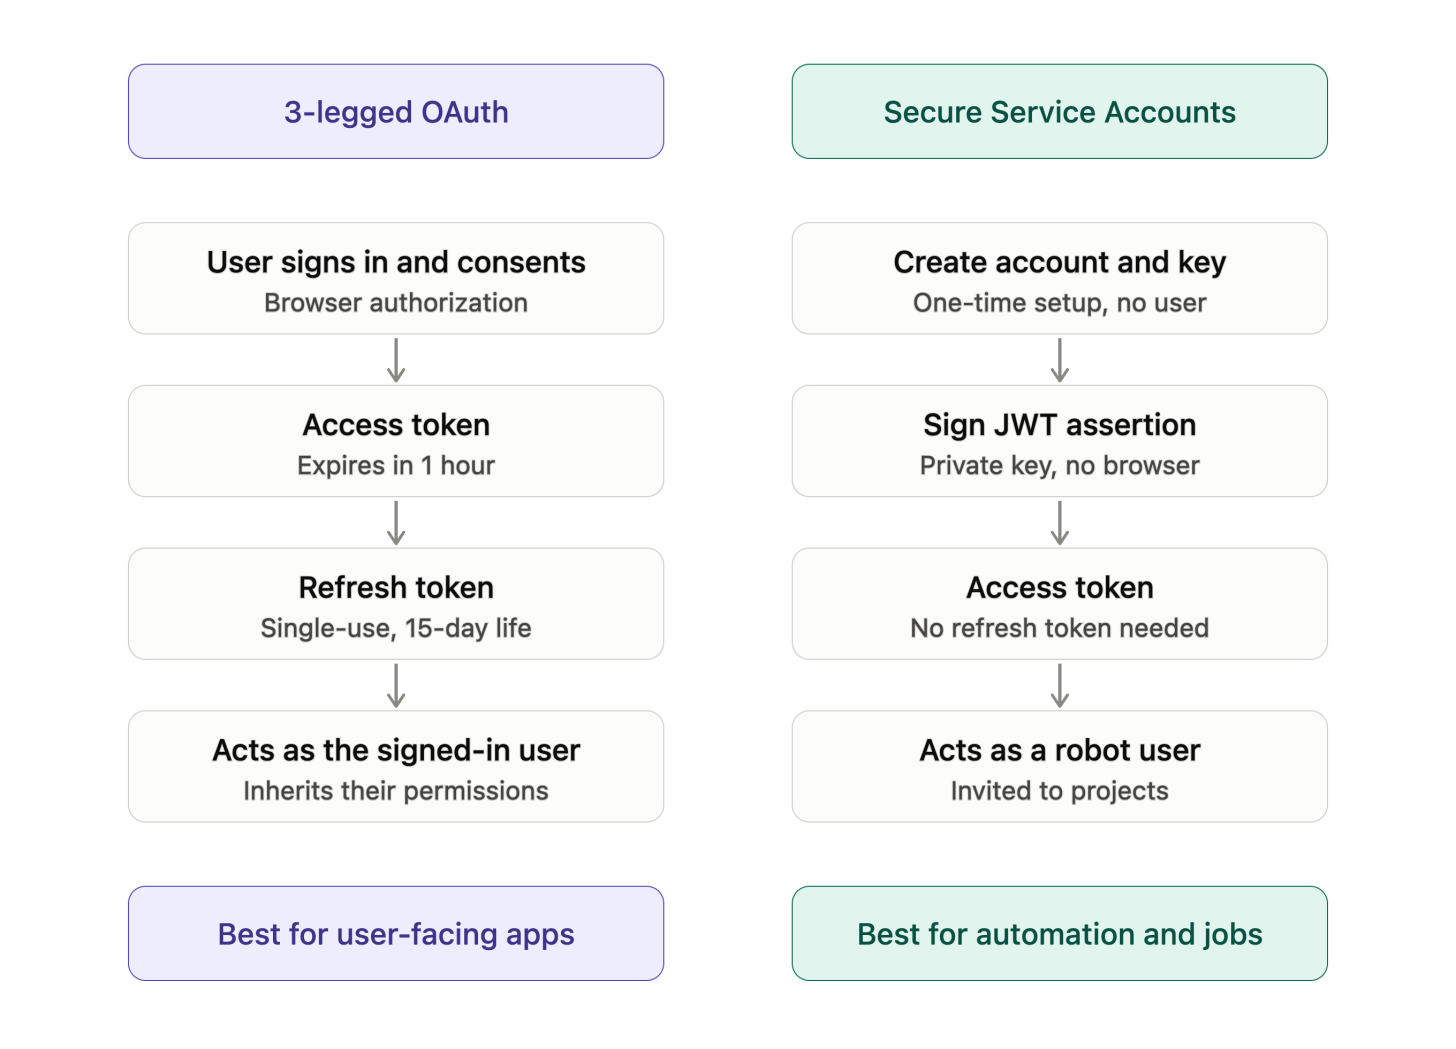
There is a detailed blog post on Secure Service Accounts, but it does not discuss when to use normal 3-legged authentication instead of Secure Service Accounts.
As the above picture shows, if you need to do things on behalf of a specific user and the operations take place while the user is running your application, then relying on normal 3-legged authentication is fine. Since the user is in front of your application, even if the token refresh goes wrong, you can ask them to log in again - it should not cause any major issues.
The main problem is if you are trying to do things on a user's behalf while they are away from your app, e.g. running automation tasks on a server. Then if the token refresh goes wrong, you might not be able to get the user to log in quickly enough, which can cause system downtime.
The bottom line:
- 3-legged OAuth: Best for user-facing apps
- Secure Service Accounts: Best for automation and jobs